

You might have heard about GDPR compliance, but don’t know much about it. But don’t worry, here’s an ultimate guide on GDPR and how to ensure GDPR compliance in your WooCommerce store. We’ll start from the basics so even a beginner can manage WooCommerce GDPR compliance like a pro.
What is GDPR?
The General Data Protection Regulation is a regulatory law for data protection and privacy in the European Union and the European Economic Area. GDPR is an important element of the EU privacy law. It is said to be the toughest security law in the world. The regulation came into effect on May 25, 2018. It is a crucial component of EU privacy law, imposing severe fines on violators of its privacy and security requirements, including those related to GDPR cookie policy, with penalties reaching tens of millions of euros.
Why do you need GDPR Compliance?
The main aim of GDPR compliance is to protect the data of your customers and site visitors. So users will feel secure when purchasing from your store. Also, it is mandatory to carry on sales internationally, especially in the EU region. If you don’t strictly comply with GDPR laws, then huge fines will be imposed on your business.
Here are some other benefits of ensuring GDPR compliance in your WooCommerce store.
1. Increased trust and credibility
When your website is listed as GDPR compliant, your store has achieved a high level of data protection. This will increase the trust and credibility of your WooCommerce store. After all, trust is a major investment in any eCommerce business.
2. Better understanding of data flow
GDPR compliance gives a deeper understanding of user data and how it moves within the organization. This will help the sales/marketing team to use them legitimately for marketing purposes.
3. Better data management
GDPR compliance will also help you manage your user’s data, as it provides a framework for what you can continue to collect and what you cannot.
4. Brand reputation
As you all know, privacy is a key to trust. By gaining GDPR Compliance, organizations not only avoid penalties but can also increase reputation and brand value.
With that being said let’s move to the step-by-step guide on ensuring GDPR compliance.
How to ensure GDPR compliance in your WooCommerce store?
GDPR is not just for business inside the EU region. Even non-EU companies should comply with GDPR if they are dealing with customers from the EU. Here are the major things you should take care of to achieve GDPR compliance.
- Tell the user who you are
- What data do you collect?
- Why do you collect the data?
- How long do you hold the data?
- And which third parties might have access to the user data?
- Get consent from the users.
- Allow users to access the data.
- Allow users to download the data.
- Allow users to delete the data.
- Let the users know if there’s any data breach occurred.
These rules must be strictly followed. If you neglect these rules, be ready to pay millions of EUROs as a fine. Even less severe infringements can result in a fine of €10 million.
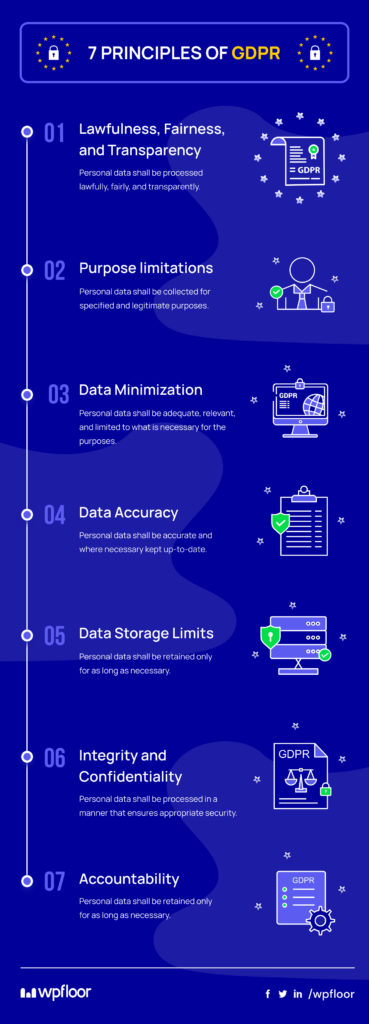
The following image will show you the 7 principles of GDPR.
Here’s the list of the biggest GDPR fines in 2021. You might be shocked to know that major tech giants like Amazon and Whatsapp have also been fined for violating GDPR. Hope you have understood the seriousness of GDPR compliance.
Here are the different steps to ensure complete GDPR compliance for your WooCommerce store.
Step 1: Privacy Policy and T&C
Your store has access to various user data including personal information, location details, and payment details. The first step is to have a proper and detailed privacy policy for your WooCommerce store. This privacy policy must have detailed information on who you are? What data do you collect? Why do you collect the data? How long do you hold the data? And which third party might have access to these data?
You can create a different page for the privacy policy page by creating a new page and linking the custom page as the privacy policy page. What WordPress provides is a template, admins can create their own privacy policy as well. Also, it is the responsibility of the admin to ensure that the privacy policy contains all the required information, especially if they are using the template provided by WordPress.
To create a new privacy policy page:
Go to Settings > Privacy in your WordPress dashboard.
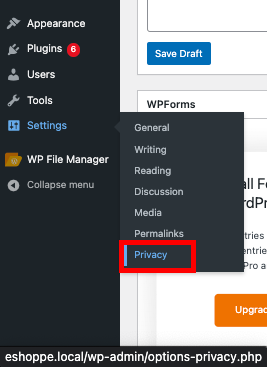
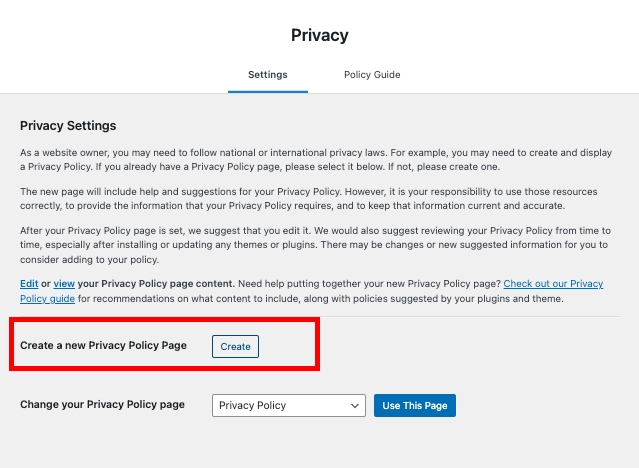
Click Create a new privacy policy page.
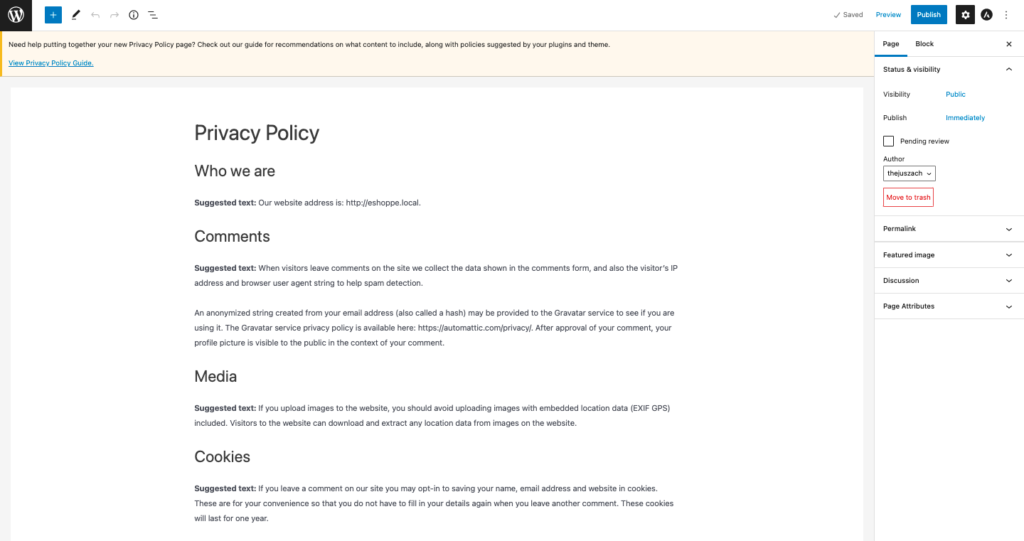
After updating the privacy policy page, click Publish to save the page.
Privacy policy and Terms & Conditions are legally bound documents but serve different purposes. Privacy Policies are aimed to protect the privacy of your customers whereas Terms & Conditions are aimed to protect your company.
Terms & Conditions are also as important as the privacy policy. You must ensure that you have shared proper Terms & Conditions with your customers to avoid a legal dispute in the future.
To create a new T&C in your WooCommerce store:
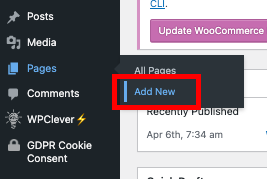
Go to Pages > New Page.
Add the Terms and Conditions in the text area.
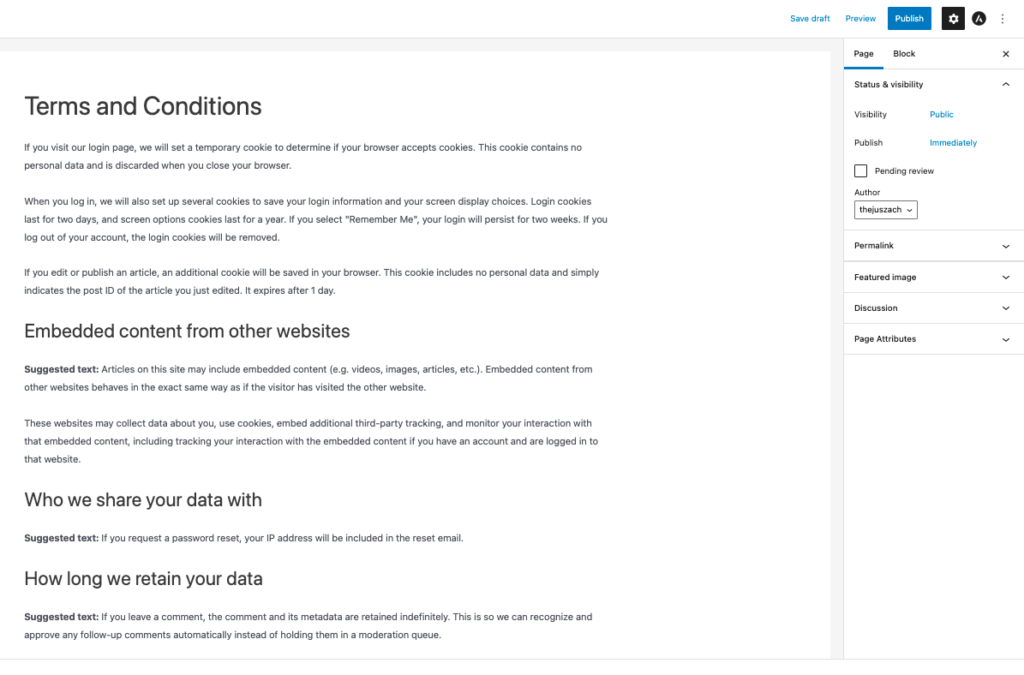
Click Publish to save the page.
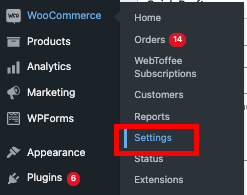
Now go to WooCommerce > Settings
Select the Advanced tab.
In the Page setup option, navigate to the Terms and Conditions
Search for the Terms and Conditions page.
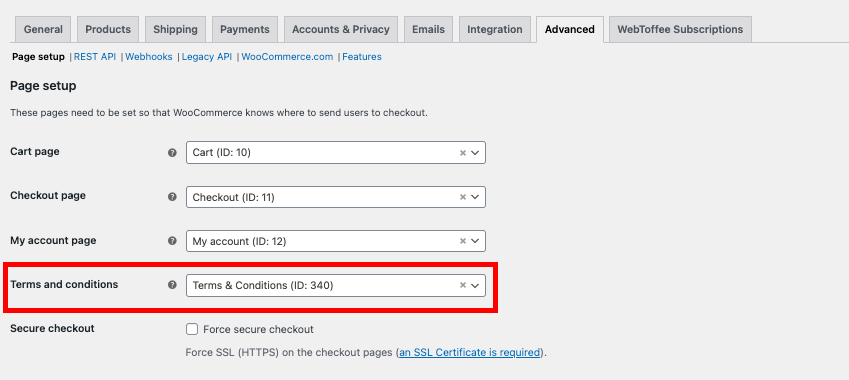
Click Save changes.
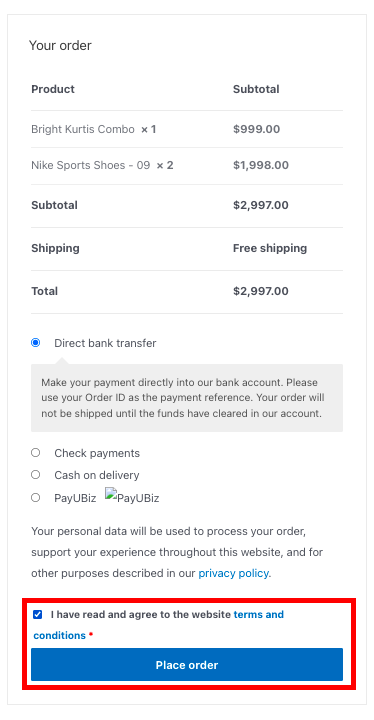
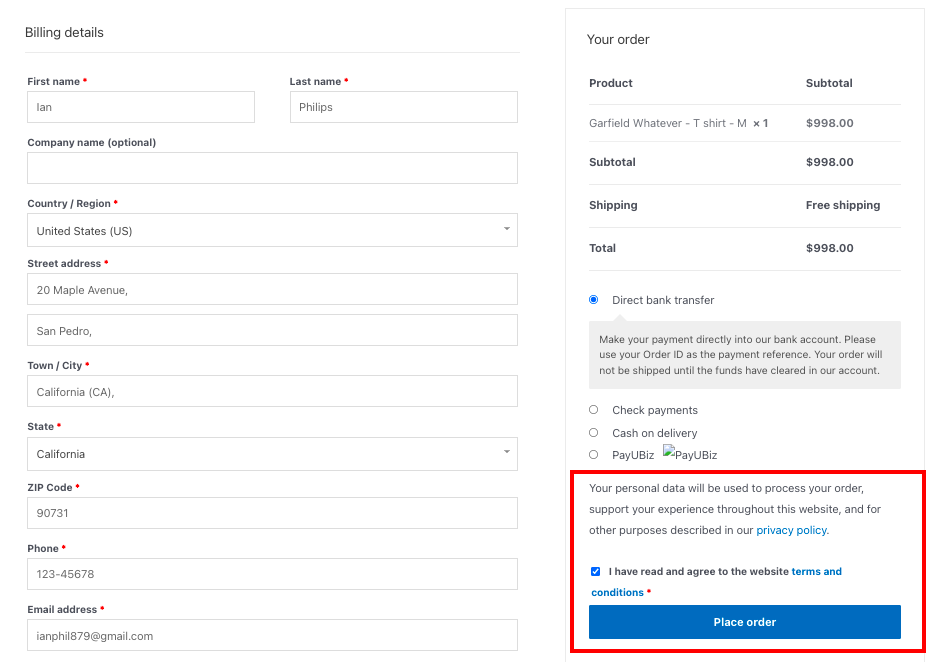
This will add a Terms and Conditions checkbox to the checkout page.
Step 2: User Data Management
Your WooCommerce site collects user data in many ways. You must ensure that the data is managed properly and you are responsible for protecting your customer data.
Here are the different ways you collect user data in your store.
- When a user registers to your store.
- When a user comments on your page.
- When a user posts a product review on your store.
- When a user fills in contact forms in your store.
- When a user opt-in for marketing emails in your store.
- Payment information including billing details, card details, etc.
Here are the measures to take for managing users’ data in your store.
User Account erasure
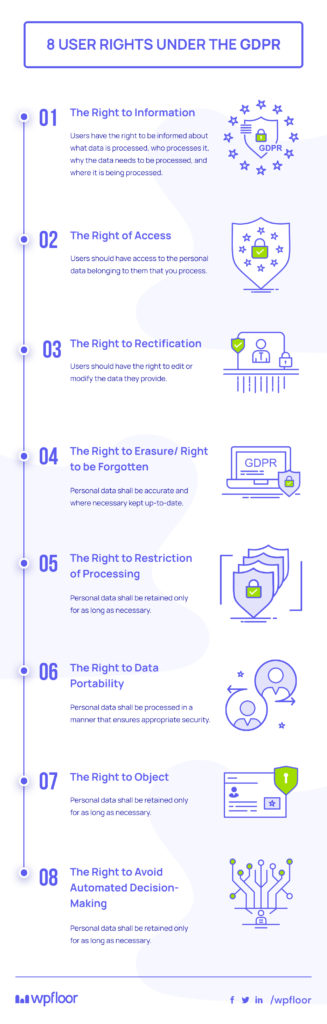
There are 8 rights for the data subjects (your website visitors in this case), among which one is the right to erasure. This means that the customers should be able to request the deletion of their personal data you collected and stored.
Here are the 8 rights for the data subjects mentioned under GDPR.
WooCommerce provides the following options to honor a user/customer’s request to delete their data.
- Go to WooCommerce > Settings.
- Select the Accounts & Privacy tab from the menu
- Enable the Remove personal data from orders on request checkbox.
- Also, enable the Remove access to downloads on request checkbox.
This allows users to remove personal data and access to download the data.
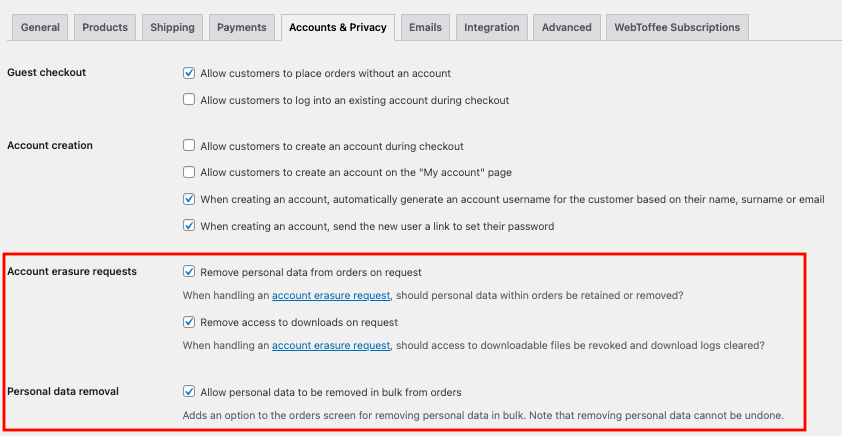
Additionally, enable Personal data removal checkbox.
Then you can edit/modify the Privacy policy in user registration and checkout.
Lastly, add the Personal data retention period as per the privacy policy of your company.
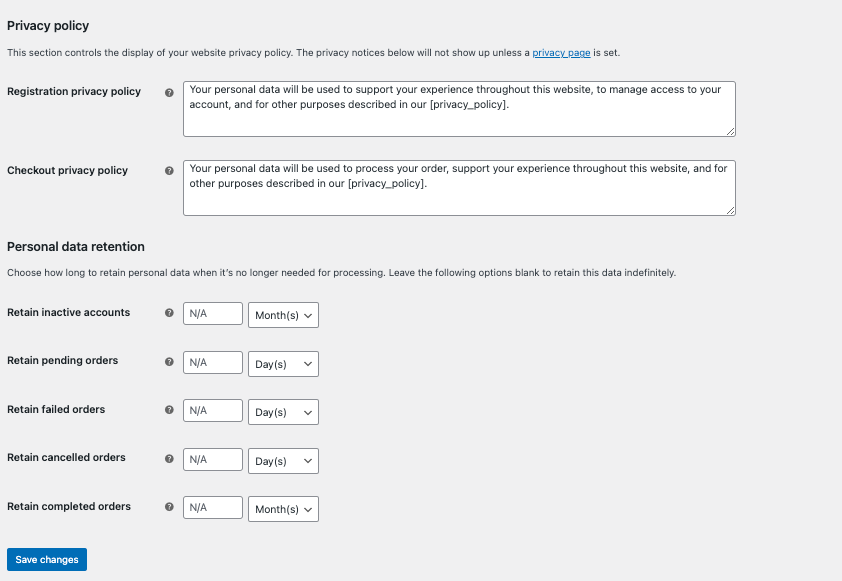
Click on Save Changes.
User profile data
When a customer posts a review on your WooCommerce store or comment on your WordPress site, the user will have to enter, Name and email address along with their review or comments without registering an account. So you must ensure that there’s a privacy policy checkbox to let the users know about collecting the data.
For product reviews:
- Go to Wooommerce > Settings > Products.
- Enable Reviews can only be left by “verified owners” checkbox.
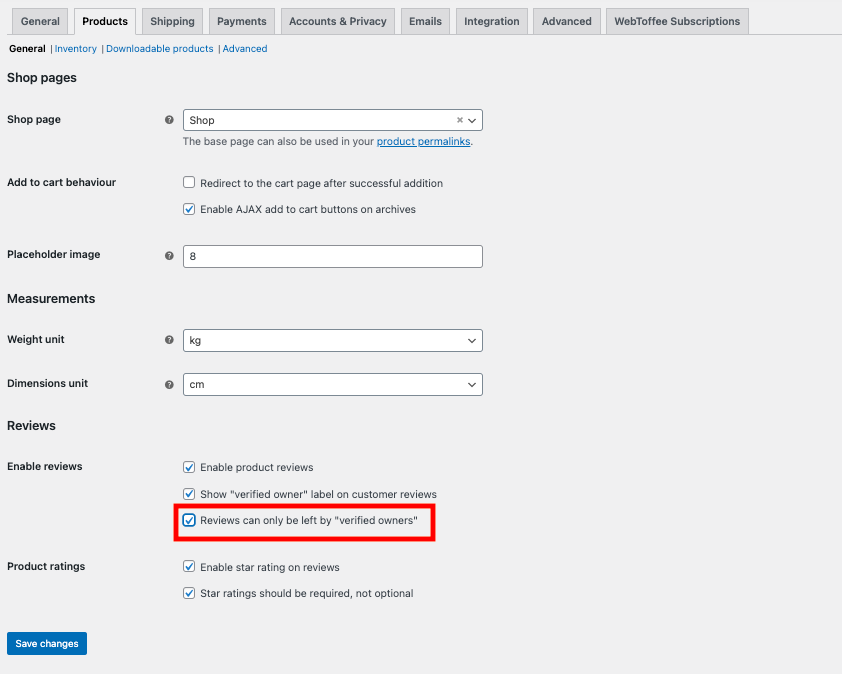
Verified customers have already opted into your Privacy Policy and Terms & Conditions while creating an account. If you want to allow reviews from non-registered users, then add a Privacy Policy checkbox to the product review page.
User Data collected through contact forms and marketing email opt-ins
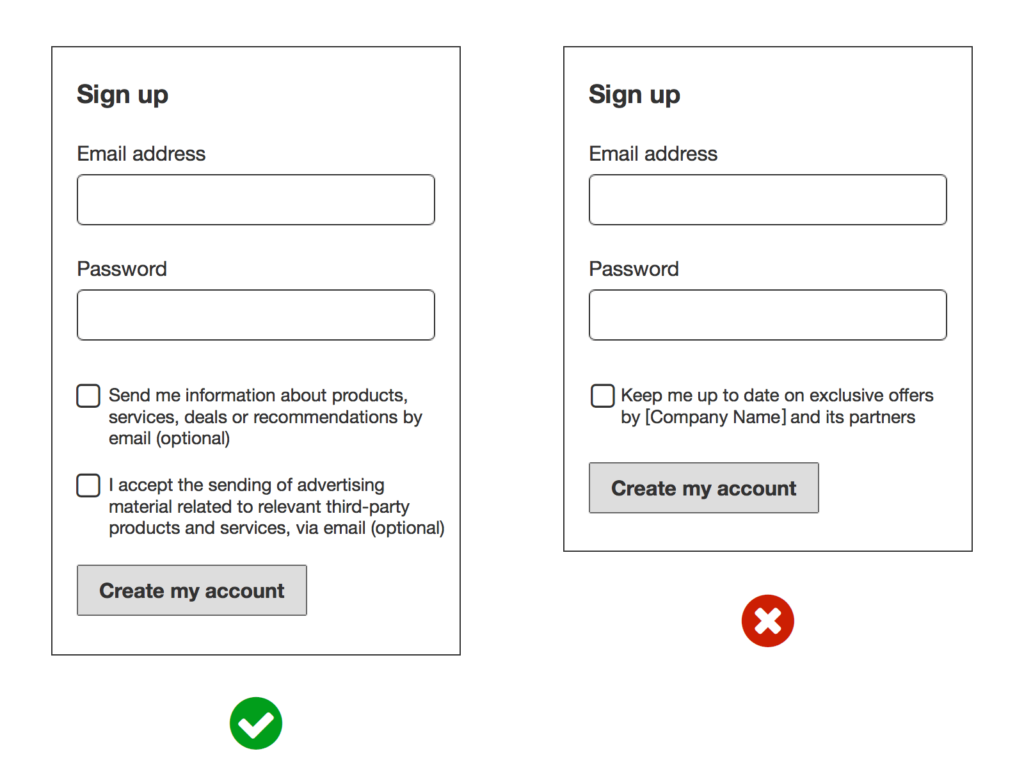
Your WooCommerce store may have a Contact Us page as well opt-in customers for receiving marketing emails. In both situations, you must get consent from the users to collect their data and use them for marketing purposes. If you are using any plugins make sure that they are GDPR friendly.
Payment data
Users share their most sensitive data on the checkout page where they add their payment details, debit/credit card details, etc. The best thing you can do here is to not store the payment details. If you don’t need them, don’t store them! Payment providers will store the data on your behalf, but you should ensure that their privacy policy complies with GDPR. Also, it would be better if you link their privacy policy to your privacy policy.
Step 3: WooCommerce Plugins and API
You might have used a lot of plugins for operating your WooCommerce store efficiently. You should ensure that all the plugins and API (Application Programming Interface) you use in your WooCommerce store are GDPR friendly.
Usually, plugins do provide this information on their product pages. If this information is not available, contact the plugin vendors to make sure that their plugins are GDPR compliant or have taken the necessary steps.
Step 4: WooCommerce Analytics
Like every other website, you may also have enabled analytics to monitor the web traffic in your store. There are various analytics tools available, but you should check with their GDPR policy, because they are collecting user data on your behalf, so it’s your responsibility to take care of the user data they collect.
Step 5: Notify the customers about data breaches if occurred
Yes, this is very important. If there’s a data breach occurred on your website, you must inform your users within 72 hours. Let them know, about the data breach and what all data were breached. Also let them know, all steps and measures you’ve taken to protect their data.
A data breach may occur in various ways:
- When the user data is passed to an unauthorized data processor or subcontractor.
- When the user data is shared with a non-GDPR compliant body
- When a third party accessed the data without the knowledge of the users.
- A hacker illegally breaches the network security and accesses the data.
GDPR Cookie Compliance
Website cookies are one of the most common ways for personal data to be collected. They are used to track user behavior and user data across the web by third parties. This data is mostly used for targeted advertising. So being aware of the cookies and their usage plays a vital role in GDPR compliance for websites.
Cookies most often collect information that GDPR considers personal data, and so your website is required to comply with the GDPR when using cookies. Under GDPR, a website must only collect personal information from users after they have given their explicit consent to its use for specific purposes.
To comply with GDPR requirements when it comes to cookie usage, websites must adhere to the following:
- Obtain prior and explicit content from users before activation of cookies.
- Users should have been given the option to partially accept the cookies.
- Users shouldn’t be forced to give their consent.
- Allow users to withdraw their consent at any moment.
- Store the consent as a legal agreement.
- Renew the consent at least once a year.
Usually, GDPR Cookie compliance is achieved through a cookie banner. Website owners use cookie banners to inform their users about the data they collect. Check out this article to learn more about WordPress cookies.
Note: You don’t have to take consent for cookies that are considered necessary for the functioning of the website and do not collect any user data. However, it is best to inform the users of the cookies and what their purposes are when users visit your website.
There are a lot of plugins available in WordPress used for acquiring GDPR compliance through a cookie banner, but we find GDPR Cookie Consent plugin to be the most useful.
Step 1: Plugin Installation
Open your WooCommerce dashboard.
Go to Plugins > Add New.
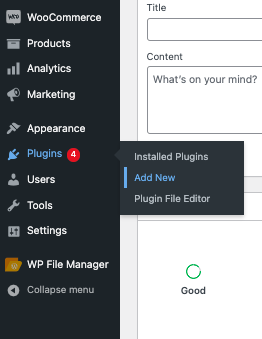
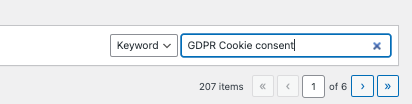
Search for GDPR Cookie consent in the plugin directory.
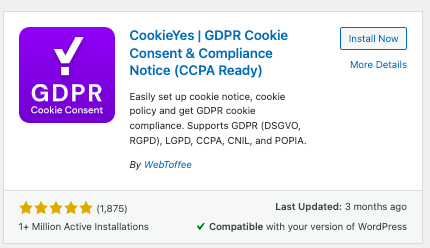
Install and Activate GDPR Cookie Consent & Compliance plugin by WebToffee.
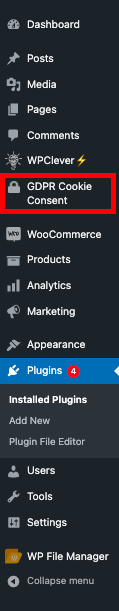
This will add GDPR Cookie Consent settings to the dashboard menu.
Step 2: Adding Cookie banner
Now, let’s add a cookie banner to our store.
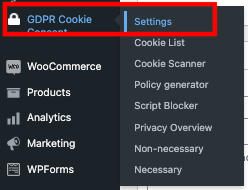
Go to GDPR Cookie Consent > Settings.
In the General tab, click on Enable cookie banner radio button.
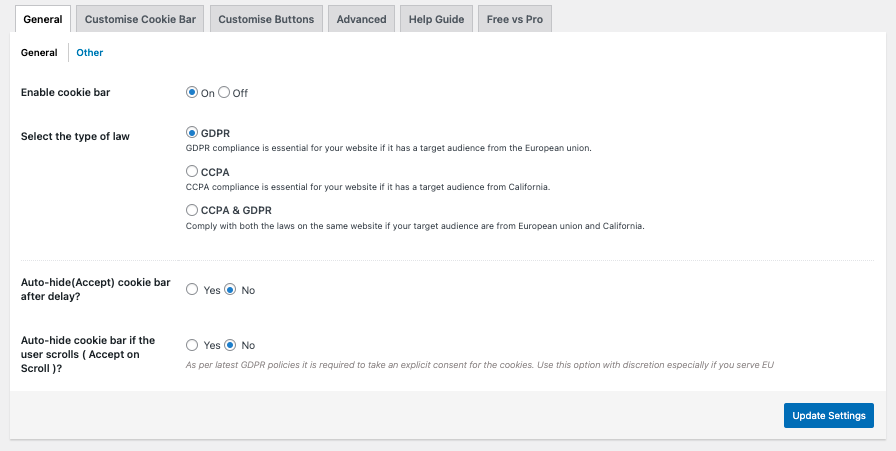
Select the type of law you want to comply with. If your target audience is from the EU, select GDPR, if they are mostly from California enable CCPA (California Consumer Privacy Act of 2018). If your target audience is from both the EU and California, you might need to comply with both laws so select CCPA & GDPR. I will select GDPR for this article.
If you want to auto-hide the cookie banner, click Yes, else No.
Click on Update Settings.
Step 3: Customizing Cookie Banner
Click on the Customise Cookie Banner tab in the plugin settings.
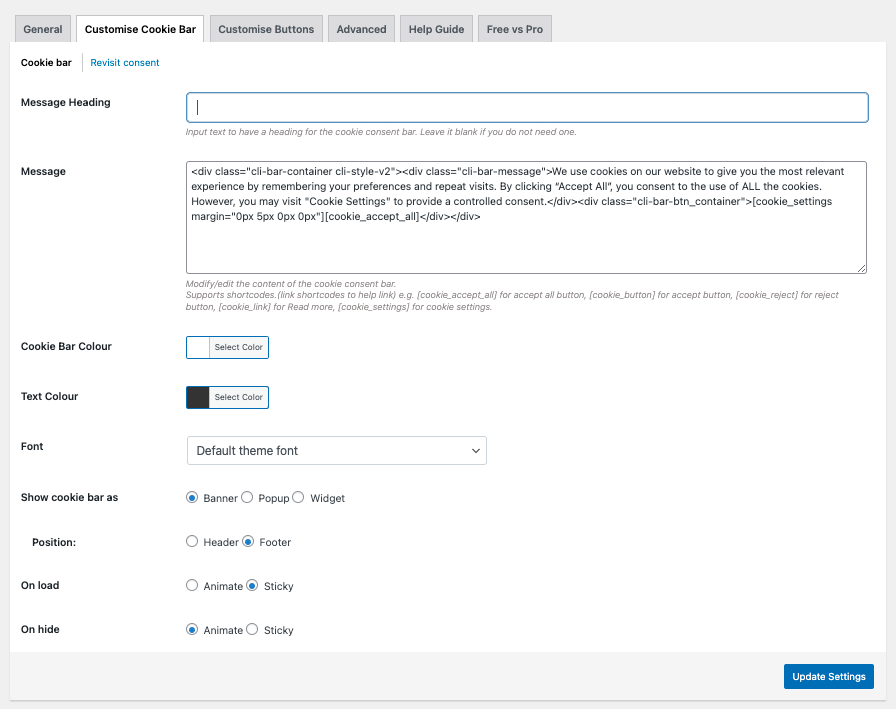
Enter a banner heading in the Message Heading text box. I’ll add Cookie Consent as a banner heading.

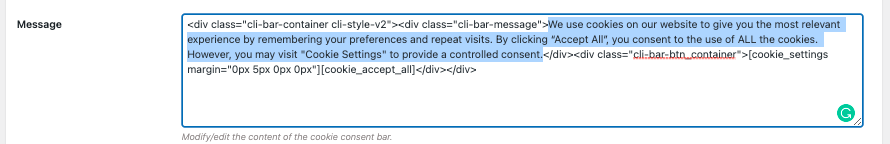
You can edit/ modify banner content in the Message text box. I’ll leave it as it is.
Select the required color for the Cookie bar and Text.
Set the font for the text in the banner. Let’s select Sans Serif for this demo.
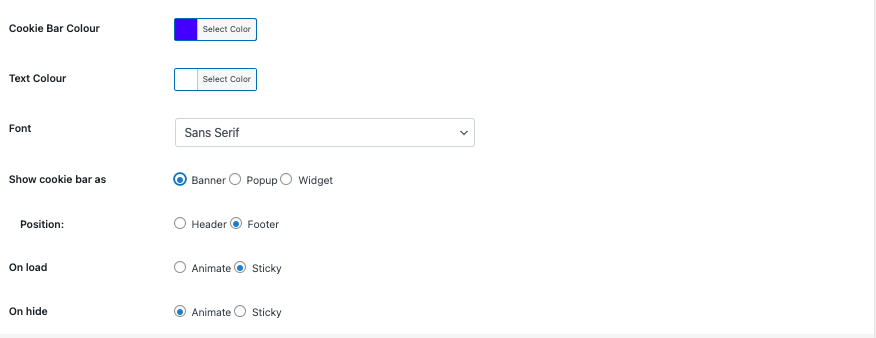
Select how you want to display the cookie banner. There are 3 options Banner, Popup, and Widget.
You can also set the position and animation for the cookie banner to display. I’ll leave them as default.
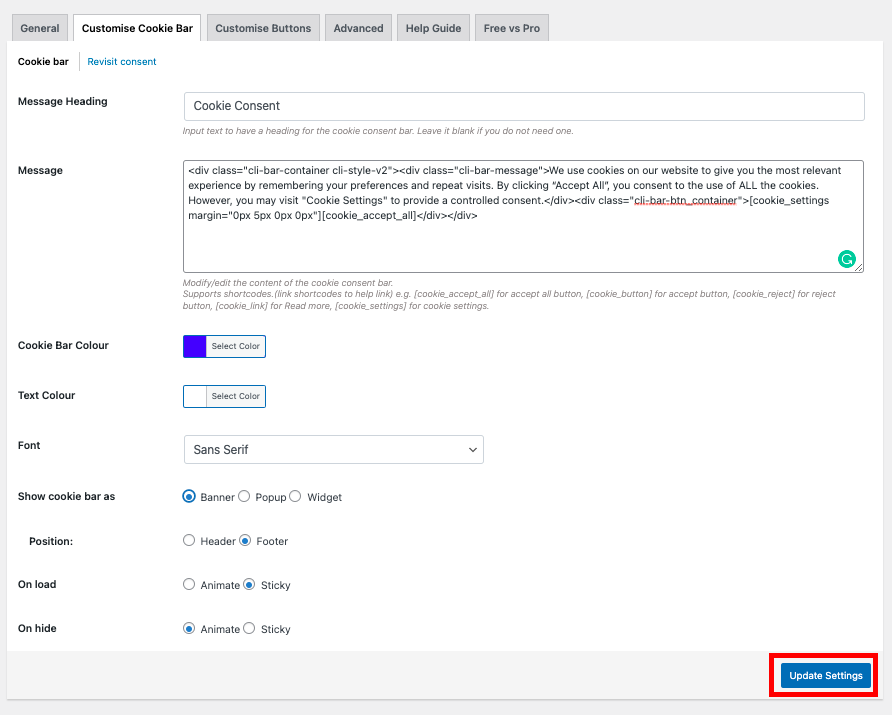
Click on Update Settings.
Step 4: Adding Buttons
By default, the cookie banner only displays Accept All button and the Cookie Settings button.
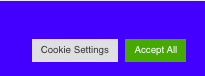
Let’s add a reject button to our banner.
Go to the plugin settings.
Click on the Customize Cookie Banner tab.
Below the Message text box, you can see the shortcodes for each button.
Here are the shortcodes:
Accept All button: [cookie_accept_all]
Accept button: [cookie_button]
Reject button: [cookie_reject]
Read more button: [cookie_link]
Cookie Settings: [cookie_settings]
Enter the required shortcode for the button in the message box.
I’ll add [cookie_reject], as I need a reject button.
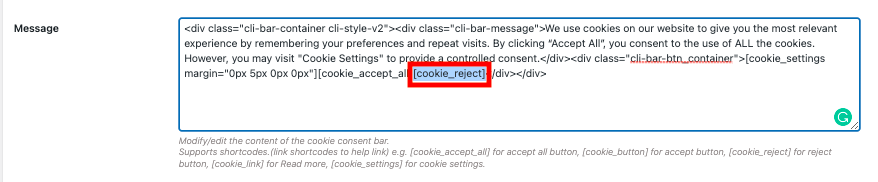
Click Update Settings to save the shortcode.
Step 5: Previewing the Cookie Banner
Go to your website.
There you can see the cookie consent banner with our applied settings.
Here’s a preview of popup style cookie banner. You can try different layouts
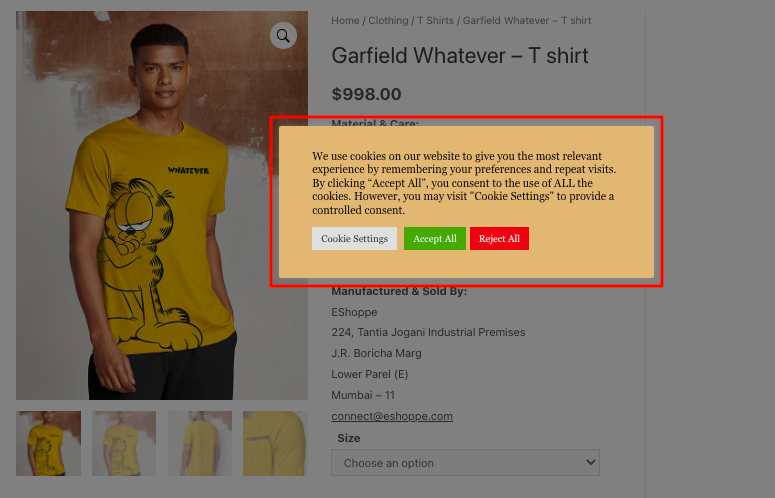
You can see the Reject button along with the Accept All button.
Refer to this article to find out the best GDPR Cookie consent banner examples.
Wrapping up:
As mentioned in this article, making your WooCommerce store GDPR compliant not only saves you from penalties but also reflects your brand reputation and people’s trust in your brand. You will also be able to better understand the user data managed by your WooCommerce store when you comply with GDPR.
I hope this article helped you in understanding GDPR Compliance and how to make your WooCommerce store GDPR compliant. If you have any doubts, please feel free to comment below.


